What Did AWS Actually Announce?
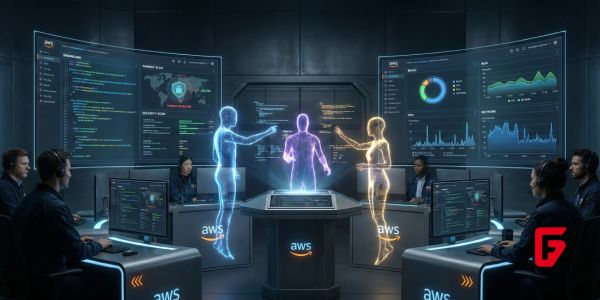
At re:Invent 2025, AWS introduced three
frontier agents:
Kiro for development,
AWS Security Agent for application security, and
AWS DevOps Agent for operations. These agents are designed to act as persistent digital collaborators that plug into your repos, pipelines, and observability stack rather than one‑off chat sessions.
AWS frames this as the next wave of enterprise AI value, moving from “assistants” that help with single tasks to autonomous systems that can drive multi‑day workflows end‑to‑end. The idea is that you tell the agent what outcome you want, and it figures out which services, repos, and configs to touch to get there.
How AWS Frontier Agents Work
The
defining capability is autonomy: these
AI agents can keep working on a problem for extended periods, maintain context, and even spawn multiple sub‑agents to tackle different parts of a task in parallel. Unlike traditional code assistants, they retain long‑term memory across sessions, learning from your codebase, documentation, tickets, and feedback over time.
They plug into everyday tools such as Git repositories, CI/CD pipelines, observability stacks, and ticketing or chat systems, letting them open pull requests, monitor tests, inspect logs, and comment in team channels as if they were human colleagues. Crucially, they propose and orchestrate changes rather than silently pushing them straight into production.
Meet Kiro, the Autonomous Coding Agent
Kiro is the development‑focused agent that behaves like an autonomous software engineer embedded in your codebase. It can handle work such as bug triage, cross‑repository refactors, and multi‑service feature implementations by planning changes, editing multiple files, and opening pull requests for review.
Kiro continuously learns from pull requests and code reviews, so its recommendations evolve with your coding standards and architecture decisions. Instead of prompting it for every file, you describe a broader problem, point it at the relevant app or repo set, and let it decide where changes should be made.
AWS Security Agent: Always‑On AppSec Partner
AWS Security Agent is positioned as a virtual application security engineer that operates from design to deployment. It can review architecture and design docs, scan code and pull requests, and perform on‑demand penetration‑style assessments in hours instead of the weeks it typically takes to schedule and execute manual tests.
Early users report that the agent can surface subtle business‑logic issues that traditional scanners miss, such as logic flows that leak data or violate internal policies. Because it is context‑aware—understanding your application design, security requirements, and custom rules—it can prioritize findings and propose concrete fixes rather than dumping generic vulnerability lists.
AWS DevOps Agent: 24/7 Ops Teammate
The AWS DevOps Agent behaves like a seasoned DevOps engineer on call around the clock, watching logs, metrics, and incidents. It integrates with monitoring tools such as CloudWatch and popular third‑party observability platforms, reads runbooks, and can orchestrate remediation steps across environments.
In one reported test, a large bank recreated a complex network and identity management issue, and the DevOps agent identified the root cause in under 15 minutes—work that would normally occupy senior engineers for hours. The goal is not just faster incident triage, but continuous reliability improvements as the agent learns from past outages and near‑misses.
Safeguards, Limits, and Human Control
Despite the “runs for days” narrative, AWS emphasizes that human engineers keep final say over production changes. The agents can open pull requests, propose configuration updates, and recommend operational actions, but they do not directly commit to production by default.
Teams can also inspect and prune the agents’ knowledge, effectively redacting sensitive sources or outdated patterns from what the agent is allowed to use. Activity can be monitored in real time, with engineers able to step in, redirect, or halt an agent’s work stream if something looks off.
How This Changes the Developer Workflow
For many teams, the shift is from prompt‑driven assistance to objective‑driven automation: you describe the desired state, and the frontier agents handle the grind across development, security, and operations. Routine but complex tasks—like propagating a breaking API change through dozens of microservices or running deep security reviews on every release—become continuous, background processes.
That creates space for engineers to focus on architecture, product thinking, and governance, while agents handle the repetitive analysis and execution that used to clog sprints and on‑call rotations. At the same time, it raises new questions about trust, review practices, and skill expectations for developers who will increasingly be supervising autonomous systems rather than doing every change by hand.
Where AWS Stands in the AI Agent Race
This move drops AWS directly into competition with other
agentic AI initiatives from players like Microsoft and IBM that are also pushing long‑running agents for coding, security, and operations. AWS is leaning hard on its
deep integration with existing cloud services and observability tools as a differentiator, aiming to make these agents feel native to complex enterprise environments.
The agents are currently in preview, with DevOps and Security Agent accessible ahead of Kiro’s fully autonomous capabilities, which are rolling out more gradually. For now, the most realistic near‑term impact will be in high‑scale organizations that already live deeply inside AWS and can pilot these agents where the operational surface area is biggest.
Sofia Klein is a Staff Writer at futureTEKnow, writing about European AI ecosystems, safety research, and the regulatory frameworks shaping how AI gets deployed.